
The growing threat of cybercrime
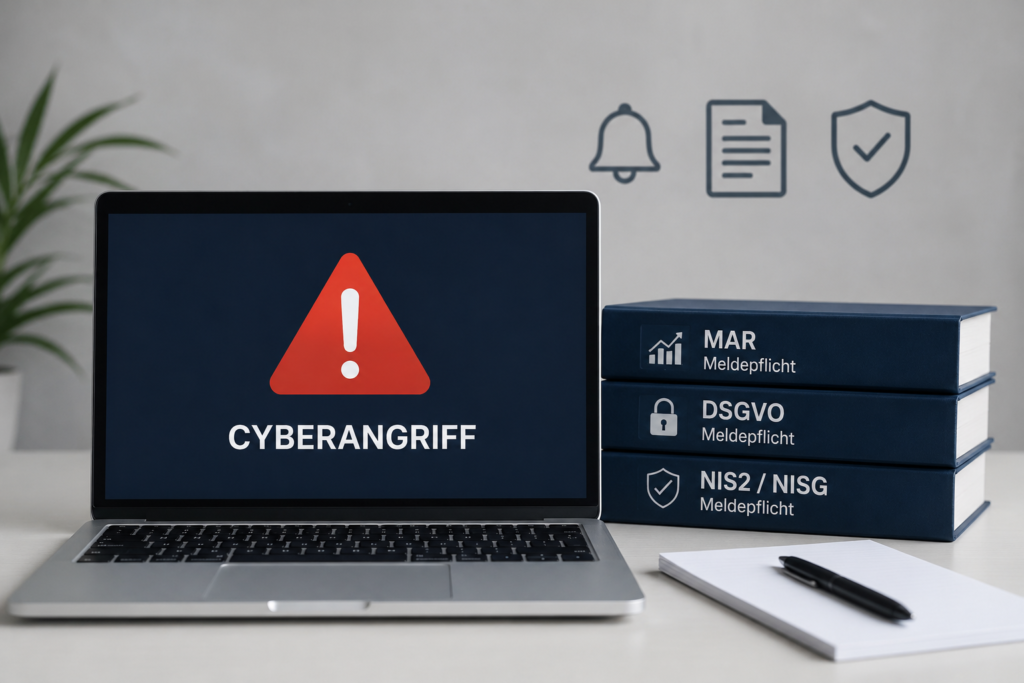
Cybercrime is one of the greatest challenges for businesses and institutions in the digital age. The Acronis Cyberthreats Report 2024 shows an alarming increase in cyberattacks worldwide. In particular, the number of Email-based attacks has risen by nearly 200 %. In addition, cybercriminals are increasingly using artificial intelligence (AI), um Phishing attacks to perfect and infiltrate IT systems. Read the full report here.
In this context, companies face the dual challenge of protecting themselves against technical threats and to protect at the same time legal requirements to fulfill.
The importance of compliance in the fight against cybercrime
In view of this threat situation, gains Compliance increasingly important. Companies are legally obligated to strict Data protection and security standards to comply with. Violations of these regulations can not only heavy fines, but also Loss of reputation entail.
A central set of rules is the General Data Protection Regulation (GDPR), which obligates companies to securely manage personal data. This includes measures such as:
- Technical and organizational security measures (e.g., encryption and access restrictions)
- Data breach notification within 72 hours
- Appointment of a Data Protection Officer, if necessary
- Documentation and proof of compliance
In addition to the GDPR, there are industry-specific security standards such as ISO/IEC 27001, which ensures an effective information security management system.
Cybersecurity measures for risk minimization
In addition to complying with legal requirements, companies must implement effective security strategies to protect themselves against cyber attacks. The most important measures include:
- Employee training: Awareness for social engineering, phishing, and other attack vectors.
- Multi-Factor Authentication (MFA): Additional security layer for accessing critical systems.
- Regular safety inspections: Penetration tests and security audits to identify vulnerabilities.
- Deployment of AI-based security solutions: AI can help detect suspicious activity early and prevent attacks.
- Emergency plans and incident response teams: Rapid and coordinated action in the event of a security incident.
Legal support and advice on cybercrime
The growing complexity of cyberattacks requires not only technical, but also legal expertise. Companies should contact us early on if there is a suspicion of cybercrime specialized attorneys for IT and data protection law turn to. These assist, among other things, with:
- Analysis and documentation of cyberattacks
- Notification of data protection incidents to supervisory authorities
- Enforcement of claims against cybercriminals
- Defense against official audits or data protection violations
For questions regarding cybercrime and compliance, the law firm ATB.LAW available as a competent contact partner. Contact us at office@atb.law or by phone at +43 1 3912345.
Conclusion: Proactive action is crucial
The threat of cybercrime is steadily increasing, and companies must continuously adapt their security and compliance strategies. Compliance with legal requirements such as the GDPR as well as the implementation of modern security measures, are essential to protect data and systems.
The combination of technological protection measures, Employee training and the collaboration with legal experts provides the best protection against cyber attacks. Only through a holistic strategy can companies master the challenges of the digital world and successfully defend themselves against cybercrime.