Brief conclusion
The draft fundamentally requires automated tools or a combination of automation and manual control for both testing steps. Purely manual checks remain permissible only if justified by the size, business model, complexity, or nature of the business. At the same time, the draft defines clear triggers for when screening must be repeated. For smaller obligated entities in the non-financial sector, this is the most noticeable cost factor of the entire set of rules.
Part 1: Identification of Politically Exposed Persons
Who needs to be tested
The draft does not limit the review to the customer. Included are:
- the customer himself,
- the beneficial owner of the customer,
- where applicable, the person on whose behalf or for whose benefit a transaction or activity is carried out.
It must be examined in each case whether the person is a politically exposed person, a family member within the meaning of the AMLR, or a known close associate.
When it must be checked
The draft distinguishes between two situations.
Prior to establishing the business relationship or carrying out the occasional transaction. Except in the cases of Art. 44 AMLR.
Ongoing with existing customers. Here, the draft defines three triggers:
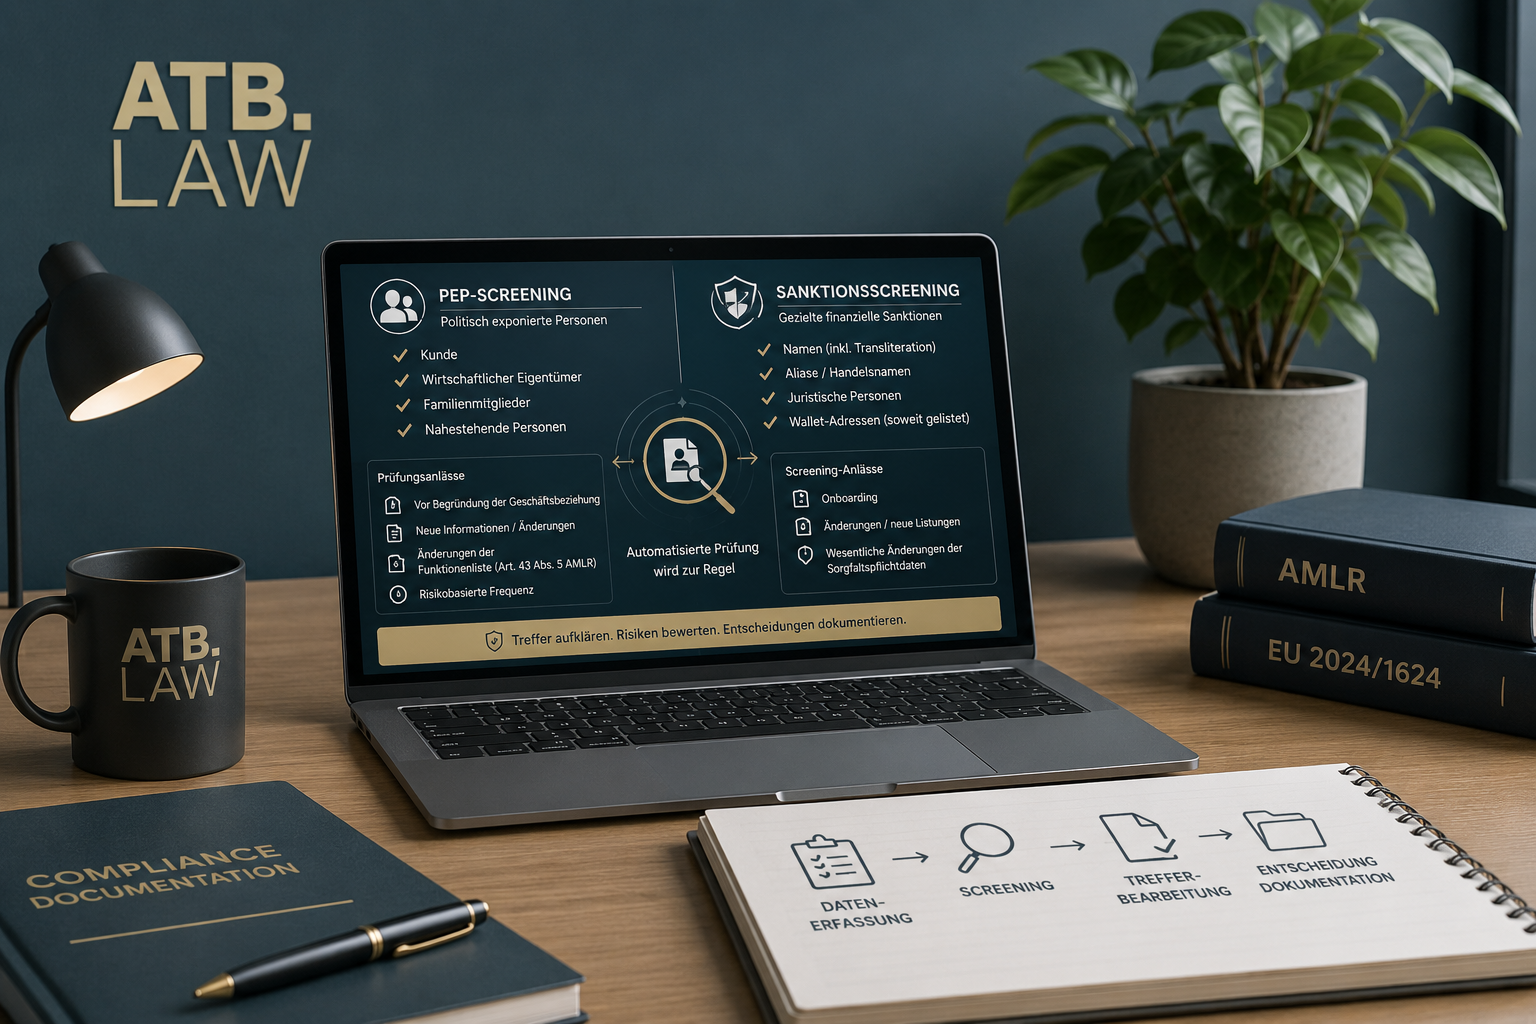
- a risk-based frequency,
- immediately upon new information or changes to the information collected as part of the due diligence obligations that may have an impact on the PEP classification,
- immediately in the event of changes and additions to the list of prominent public functions published pursuant to Article 43(5) AMLR.
The third trigger is the most practically demanding. It requires monitoring published feature lists and a process chain that immediately triggers a re-reconciliation of inventory upon changes. A purely routine screening is not sufficient.
How it must be checked
The draft requires automated screening tools and measures or a combination of automated tools and manual controls. The exception for purely manual checks is linked to the size, business model, complexity, and nature of the obliged entity's business.
This wording is a proportionality clause, not a general exemption. Anyone relying on it should document the reasoning. A sole practitioner with a few mandates per year is in a different position than a mid-sized law firm with an ongoing real estate escrow business.
Part 2: Screening against targeted financial sanctions
The test circuit
The draft obliges the determination of whether customers, beneficial owners, as well as those legal entities or persons who control the customers or meet the ownership requirements of Article 20(1)(d) of the AMLR, are subject to targeted financial sanctions.
If there is a suspicion of circumvention or avoidance, it must additionally be checked whether the person acting for the customer is subject to sanctions. The representative is therefore not routinely included in the scope of the check, but is included if there is a suspicion of circumvention.
Which data fields are to be reconciled
The draft explicitly names the screening fields:
- for natural persons, all first and last names, in the original and/or in transliteration,
- for legal entities the registered name, in the original and/or in transliteration,
- for natural and legal persons, entities or bodies, additional names, aliases or trade names, insofar as they differ from the registered name, as well as Digital wallet addresses, insofar as they are included in the sanction lists.
The inclusion of wallet addresses in the catalog of screening fields is the most notable innovation. It transfers a practice that was previously established primarily in the crypto sector into the general screening standard. Obligated entities that accept or process crypto assets require data sources and processes for this that go beyond traditional name screening.
Handling Hits
In the event of a hit, the screening data must be compared against all available due diligence information to determine whether the person is indeed the subject of the sanction. In case of doubt, all other available sources must be consulted, including public sources such as registers of owned or controlled legal entities as well as central registers.
This is a rejection of purely list-based hit processing. Resolving a potential hit is an analytical task, not a click path.
Screening occasions
The draft names three minimum occasions for screening:
- during onboarding, or prior to establishing the business relationship or executing the occasional transaction,
- in the event of changes to existing listings or a new listing pursuant to Article 26(4) AMLR,
- in the event of material changes to the due diligence data of an existing customer, a beneficial owner, or a controlling person, such as a change of name, place of residence, nationality, or business activity, provided these may affect a listing.
Screening and review must be carried out without undue delay and based on updated sanctions lists.
An important distinction
The recitals clarify that trade and economic sanctions, such as arms embargoes, trade restrictions, or travel bans, do not fall within the scope of the AMLR and therefore not within that of the draft either. The RTS exclusively regulates targeted financial sanctions within the meaning of Art. 2 (49) AMLR.
This demarcation does not provide relief. It merely shifts the legal basis. In Austria, obligations to implement international and EU sanctions arise from the sanctions law framework and directly applicable EU regulations. Obligated parties therefore require a screening concept that covers both levels and cleanly separates the respective legal bases.
Data quality determines screening quality
The draft requires elsewhere that all first and last names be collected in accordance with identity documents and that address information follows a defined structure. These requirements appear formalistic, but have a direct impact on the screening.
An incompletely recorded middle name, a missing transliteration of a Cyrillic name, or an unrecorded trade name lead to false-negative results. Conversely, unstructured data generates false-positive matches and ties up processing capacity.
Data cleansing in the existing inventory is therefore not a side project, but a prerequisite for functioning screening.
Liability and criminal law dimension
Violations of sanctions regulations are punishable by law in Austria. In addition, there are regulatory sanctions and, in cases involving money laundering, the connection to Section 165 of the Austrian Criminal Code (StGB) (see in this regard here).
For the defense, it is crucial that a documented, traceable review process exists. A screening concept that records the triggers, the lists used, hit processing, and decision-making paths is regularly the most important evidence of exoneration in proceedings.
Practical checklist
- Match screening fields. Are aliases, trade names, and transliterations captured? Is a field provided for wallet addresses?
- Implement triggers. Does the change to the list of functions pursuant to Article 43(5) AMLR actually trigger a portfolio reconciliation at your end?
- Ensure list up-to-dateness. How soon after a new listing is screened?
- Document hit processing. Who decides, on what basis, within what timeframe?
- Justify the proportionality decision. If screened manually, the justification must be in writing.
- Clarify distinction from trade sanctions. Both levels need a jurisdiction.
Your next step
The classification of a business relationship as low or high risk determines the effort and liability involved. The certified anti-money laundering attorneys at ATB.LAW assist in designing risk-based due diligence processes, defining catalogs of evidence, and handling documentation for regulatory authorities.
Write to us: Anela Blöch (bloech@atb.lawRoman Taudestaudes@atb.law)
FAQ:
Do I have to use automated screening software as a small business?
The draft requires automated tools or a combination with manual controls. Purely manual checks remain permissible if justified by the size, business model, complexity, or nature of the business. The justification should be documented.
How often must the inventory be checked for PEP characteristics?
The frequency must be determined on a risk-based approach. In addition, an immediate review must be conducted if new information is available or if the list of important public offices pursuant to Art. 43(5) AMLR is amended.
Will wallet addresses be part of sanctions screening in the future?
Yes, insofar as they are included in the targeted financial sanction lists. The draft explicitly names digital wallet addresses as a screening field.
Must the authorized representative also be screened?
The draft provides for this if there is suspicion of the circumvention or avoidance of targeted financial sanctions.
Do trade sanctions and travel bans fall under the RTS?
No. The recitals clarify that trade and economic sanctions fall outside the scope of the AMLR and thus of the draft. They arise from other legal bases.
What to do in case of a hit?
The match must be checked against all available due diligence information. In case of doubt, additional sources, including public registers, must be consulted. The decision must be documented.