Brief overview
- The draft is a Level 2 legal act under the AMLR and, as a Commission delegated regulation, will apply directly in all Member States.
- The public consultation ran until May 8, 2026. It is closed.
- Article 28(1) AMLR provided for the submission of the final drafts to the Commission by July 10, 2026.
- The AMLR itself will apply from July 10, 2027. Until then, processes, systems, and internal guidelines must be adapted.
- The draft applies horizontally, meaning equally to the financial and non-financial sectors.
Where the draft stands within the legal framework
The 2024 EU anti-money laundering package consists of three building blocks: the AMLR as a directly applicable regulation, Directive (EU) 2024/1640 (AMLD6), and the AMLA Regulation (EU) 2024/1620. The AMLR shifts the substantive obligations of obliged entities from the national implementation level to the regulation level. This eliminates the previous leeway that was previously filled by the Austrian Financial Market Anti-Money Laundering Act (FM-GwG), the Trade Act (Gewerbeordnung), the Lawyers' Act (Rechtsanwaltsordnung), and the Notaries' Act (Notariatsordnung). (regarding money laundering in Austria – defense against suspicion or charges – see here).
However, the AMLR remains abstract in many places. This is precisely where Article 28(1) AMLR comes in. The provision obliges AMLA to develop technical regulatory standards that specify:
- what information must be collected for standard, simplified, and enhanced due diligence,
- what risk factors regulatory authorities must take into account when exempting certain e-money instruments,
- which reliable and independent sources of information may be used for identity verification,
- what attributes electronic identification means and qualified trust services must have.
In practical terms, this means that the Level 2 text determines the benchmark against which regulators will measure compliance practices.
The origin story explains the content
The draft is not a new creation. On March 12, 2024, the Commission had commissioned the EBA to carry out the preparatory work by means of a call for advice. The EBA conducted a three-month consultation and a public hearing, in which, according to AMLA, more than 600 stakeholders participated. 170 written comments were incorporated into the revision. On October 30, 2025, the EBA submitted its response together with the draft RTS.
At the same time, the Commission established a sub-group of its expert group on money laundering and terrorist financing covering the non-financial sector. Its work was transferred to AMLA in September 2025.
AMLA has largely adopted the EBA text and made only selective changes. This was a deliberate choice. In the consultation paper, AMLA justifies this with continuity, the consensus already achieved among supervisory authorities, and the goal of swift adoption. AMLA has also published the EBA draft in a version with tracked changes.
For practice, this results in an important point: the content direction of the future Level 2 law is already recognizable. Anyone who waits for the final text will lose preparation time.
A set of rules for all obligated parties
AMLA has examined whether separate standards for the financial and non-financial sectors would make sense. The authority decided against it.
The argument is that due diligence obligations do not differ by industry, but by risk. Understanding an ownership and control structure does not change depending on whether a bank or a real estate agent is screening. In AMLA's assessment, two separate regulatory frameworks would have led to fragmentation, duplicate compliance costs for cross-sector companies, and slower adjustments.
The draft therefore contains horizontal rules, supplemented by a few sector-specific provisions, for example on collection accounts of credit institutions and on the distribution of units by collective investment undertakings.
This is particularly relevant for Austria. The AMLR significantly expands the circle of obliged entities. In the future, this will include, among others, crowdfunding service providers, operators of investment migration programs, football clubs and football agents, mortgage and consumer credit intermediaries, non-financial mixed holding companies, and crypto-asset service providers. Many of these addressees will be subject to comprehensive due diligence obligations for the first time and will now be measured directly against a uniformly harmonized European standard.
Six points that cause effort in practice
1. Identification data becomes more granular
The draft specifies which details are to be collected concretely. In the case of natural persons, all first and last names according to the identity document must be recorded; in the case of legal persons, the registered name and additionally the differing trade name. Address details follow a defined structure with the country name or ISO 3166 code. The place of birth must be stated at least with the country, and further details in the identity document are to be adopted. All nationalities or, where applicable, statelessness as well as refugee or subsidiary protection status must be collected.
Companies that use free-text fields and inconsistent name spellings in their customer master data today have data quality work ahead of them. This has a direct impact on the match quality during sanctions screening.
2. Identity documents receive minimum features
The draft defines when a document is equivalent to a passport or identity card. Requirements include, among other things, state issuance, name and date of birth, expiration date and document number, photograph and signature, as well as security features. For individuals who cannot present such a document for legitimate reasons, the draft provides for a facilitated catalog. The explicit goal is to prevent financial exclusion and unjustified de-risking.
3. Remote identification is linked to eIDAS
For identifications without personal presence, the draft provides for the priority of electronic identification means pursuant to Regulation (EU) No 910/2014 with the security levels „substantial“ or „high“ or qualified trust services. Only when such solutions are not available or cannot reasonably be expected may other remote identification procedures be used. These must meet defined security safeguards. Obligated entities must be able to justify to the supervisory authority why the priority path was not feasible.
4. Registers alone are not enough
According to the recitals of the draft, querying central registers of beneficial owners is necessary, but not sufficient. The draft therefore lists appropriate additional measures, such as querying other public registers or obtaining information from the customer and from third-party sources.
In Austria, this directly affects the practice of the WiEReG query. The register extract remains a central component, but cannot replace the verification.
5. Complex structures receive a definition
The draft defines complex corporate structures based on a combination of at least three tiers between the client and the beneficial owner, as well as other characteristics such as legal arrangements or foundations within a tier, registrations outside the EU, nominee structures, or obfuscation without economic justification. In these cases, additional information must be obtained, such as an organizational chart.
Notable is the clarification regarding the management level: The identification of senior executives instead of beneficial owners is only permissible if all possible means have been exhausted or doubts exist. The mere difficulty in complex structures is expressly not sufficient.
6. Automation becomes an expectation
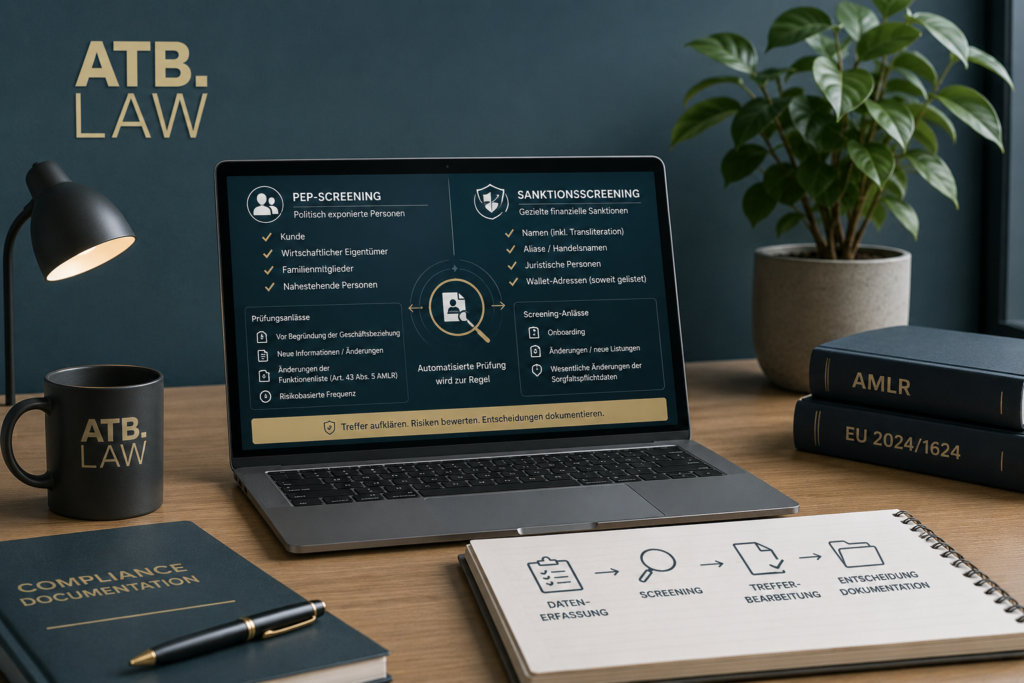
For the identification of politically exposed persons as well as for screening against targeted financial sanctions, the draft requires automated tools or a combination of automation and manual review. Purely manual reviews remain permissible only if justified by size, business model, complexity, or the nature of the business.
For smaller law firms, brokers, and commodity traders, this is a point with a noticeable cost impact.
Procedural status and open items
According to the overview of regulatory instruments maintained on the AMLA website, last updated on July 21, 2026, the RTS pursuant to Art. 28 para. 1 AMLR is listed as having the status of a completed consultation. A final report was not linked there at that time, unlike for other mandates, for example. Whether and in what version the text has already been submitted to the Commission cannot be conclusively deduced from this. Following submission comes adoption as a delegated regulation and publication in the Official Journal.
The application date is also open in the draft. The text contains a placeholder at this point. For existing customers, the draft provides for a risk-based adaptation, at the latest within the deadlines of Art. 26 para. 2 AMLR. According to the recitals, the maximum deadlines of one and five years respectively for legacy customers are only to begin running from the application date.
What makes sense now
- Gap analysis against the draft text. The draft is public. A comparison of the existing survey fields and audit steps can already be carried out.
- Check data quality in inventory. Name fields, address structure, nationalities, and transliterations determine the screening quality.
- Evaluate the identification route. Check whether the deployed remote identification solutions are eIDAS-compliant or if the obligation to provide a justification applies.
- Plan update cycles. The deadlines under Article 26(2) of the AMLR create a significant processing backlog for large customer portfolios.
- Schedule internal guidelines and training sessions. July 10, 2027 is a fixed deadline, not a target corridor.
- Observe national parallel development. The draft bill for a Beneficial Owners Register Act 2027 shows that the Austrian environment is also in motion.
Your next step
ATB.LAW assists obliged entities in preparing for the AMLR and the associated Level 2 legislation. As certified AML officers, we review existing due diligence processes, assess the need for adjustments, and support implementation in internal guidelines.
Write to us: Anela Blöch (bloech@atb.lawRoman Taudestaudes@atb.law)
FAQ:
Regulatory technical standards are adopted by the Commission as delegated regulations. They apply directly in all Member States. National implementation is not required.
As of when do the new due diligence obligations apply?
The AMLR applies from July 10, 2027. The application date of the RTS still contains a placeholder in the draft and will be determined upon adoption by the Commission.
Is anything changing for lawyers and notaries?
Yes. The material due diligence obligations will in future arise directly from the AMLR and Level 2 legislation instead of the Federal Lawyers' Act or the Notarial Code. The auditing standard will become more detailed and uniform throughout Europe.
The draft treats the registry query as necessary, but not sufficient. Additional appropriate verification measures are provided.
The draft requires automated tools or a combination with manual controls. Purely manual checks remain permissible if justified by size, business model, complexity, or the nature of the business.
Existing business relationships must be reviewed on a risk-based approach, at the latest within the time limits of Article 26(2) AMLR.